S/4 HANA Migration: Navigating SAP RISE, Object-Based Licensing, and Role Bloat
Taking flight to the cloud: moving to SAP RISE promises modern scalability, but carrying bloated legacy roles can inflate your cloud bill from day one.
Rise to the Cloud: What is Happening and Why It Needs Attention
A quick look at the cloud forecast before you pack your bags and move your SAP estate.
SAP is telling thousands of companies running their trusty old ECC systems that it is time to pack their bags and head over to the cloud on S/4HANA and SAP RISE.
In the old days, you bought simple user passes that didn’t change much, but under SAP RISE, everything switches to object-based licensing called Full Usage Equivalents, or FUE.
In this new cloud world, SAP does not bill you for what your staff actually do on screen, they bill you for whatever expensive buttons someone could click on paper.
Over ten or fifteen years, people in your company have collected piles of extra permissions like dust, and because nobody ever took the old keys away, user accounts are completely bloated.
If you drag those messy legacy roles straight into SAP RISE, your cloud bill can easily jump by 15% to 25% on day one, and surprise audits will catch you out.
Cleaning up your access with hard system facts before you sign your cloud contract stops the cash leak, keeps auditors smiling, and ensures minimal disruption to your daily work.
Think of your SAP access rights like house keys. When someone joins a company, they are given a front door key. A year later, they help out in the warehouse, so they are handed a warehouse key. Three years later, they help with finance, so they receive an accounts office key. Ten years down the line, that employee is carrying a massive keyring with 500 heavy brass keys clattering in their pocket.
They only ever use one single key to unlock their desk each morning, but SAP charges your company as if they walk into the high-security master vault every single day.
In the old days of SAP ECC, licensing rules were relatively relaxed. Most people were assigned broad Named User categories, and companies learned to live with the waste. But when you plan an S/4 HANA migration, especially under modern cloud contracts like SAP RISE, the rules change completely. SAP now uses object-based licensing and Full Usage Equivalents, or FUE. Under this model, every single transaction code, authorisation object, and stray permission inside a role is counted. If a user carries a single high-level permission tucked away inside an old, forgotten role, SAP automatically bumps them from an inexpensive Core tier into a premium Advanced tier.
Carrying legacy role bloat into the cloud does not just create financial headaches. It also opens up dangerous compliance landmines and external security risks:
First, there is the risk of serious Segregation of Duties conflicts, known as SoD. Over time, staff collect conflicting powers on paper. An employee in purchasing might have been given access to approve vendor payments during an emergency five years ago. On paper, that person has the power to create a fake supplier and pay money to themselves. Traditional compliance tools flag this as an active corporate fraud risk, leaving compliance managers drowning in massive, terrifying spreadsheets.
Second, there is the hidden danger of external connections. When modern third-party apps, like web shops, warehouse scanners, or expense tools, connect to your system, they create documents in the background. In S/4 HANA, SAP counts these as Digital Access. If you do not monitor this activity carefully, standard vendor audit tools will scan your database and hand you an unexpected penalty bill for millions of untracked documents.
Too often, SAP security is treated as an annoying cost centre. But with object-based licensing in SAP RISE, security becomes your primary financial lever. Every single role you optimise is an expensive licence you do not have to buy. Every toxic conflict you eliminate is a nasty audit penalty avoided. At Tango Technologies, we built TangoTec Cortex to turn security into a direct source of business savings, establishing total pricing certainty and clean governance with minimal downtime.
The Five Headaches Every SAP Leader Recognises in an S/4 HANA Migration
When an IT director or finance lead brings us in to look at their landscape, we usually find a combination of five compounding headaches:
The Named User Trap
Handing out top-tier Professional licences based on job titles or guesses, because nobody has the time to audit what staff actually run before an S/4 HANA migration.
S/4HANA Migration Gaps
Legacy transaction codes disappear in the cloud and move to Fiori web tiles, leaving project leads guessing how security roles will map across during an S/4 HANA migration.
Fluid FUE Liabilities
Under SAP RISE, your bill is not fixed. A single stray authorisation tucked inside a shared role can instantly elevate your entire company’s licence tier throughout your S/4 HANA migration.
Chronic Role Creep
A decade of staff changes leaves systems packed with dormant accounts and unmonitored privileges that nobody dares tidy up manually before an S/4 HANA migration.
Surprise Vendor Audits
Vendor audit tools scan behind the scenes for third-party systems creating Digital Access documents, delivering unexpected penalties during an S/4 HANA migration.
Why Leaving Role Bloat Alone in an S/4 HANA Migration Costs Real Money
- Subscription Price Spikes: Blindly copying old ECC security profiles into S/4HANA automatically triggers top-tier FUE rates, inflating annual cloud costs by 15% to 25%.
- Unplanned Digital Access Bills: External apps feeding sales orders or invoices into SAP create indirect documents in the background, exposing you to sudden backdated claims.
- Audit Spreadsheets That Lie: Tracking risk mitigations on desktop spreadsheets means expired controls get missed, leading to awkward moments when external auditors arrive during an S/4 HANA migration review.
- Testing Fatigue and Delays: Finding security errors late in an S/4 HANA migration test cycle forces expensive delays, extra contractor bills, and chaotic go-live weekends.
The Math in Action: Comparing a 1,000-User and a 10,000-User Landscape
Illustrative ImpactTo see how quickly small percentages turn into massive commercial leaks, consider what happens when a typical 10% licence bloat and a 10% role creep exist across two different company sizes during an S/4 HANA migration:
Mid-Sized Estate (1,000 Users)
100 inactive leavers and completed contractors still holding paid licences at an average of £750 per user.
100 staff bumped from Core (0.2 FUE) to Advanced (1.0 FUE) due to single stray permissions, wasting £960 each.
Enterprise Estate (10,000 Users)
1,000 inactive accounts across global divisions still consuming paid subscription licences every single month.
1,000 staff carrying inherited composite roles that needlessly push them into top-tier cloud pricing brackets.
The Clean-Up Dilemma: Internal Staff vs External Consultants
When IT leaders realise their system is leaking hundreds of thousands of pounds, they usually look at two traditional routes: asking their internal team to fix it, or drafting in external consultants. Both manual methods face serious operational hurdles:
If you ask your internal security team to clean up roles manually, they face an impossible task. Internal administrators already have full-time jobs handling daily password resets, joiners, and project tickets. Reviewing thousands of roles manually means scheduling endless workshops and building 2,000-row spreadsheets. When you ask business managers what access their team can surrender, they almost always say: “Leave everything as it is, just in case we need it.” The project drags on for months, causes friction with departments, and frequently stalls.
If you bring in external consultants, they will charge thousands of pounds a day to run those exact same manual interviews. They will build theoretical role definitions in spreadsheets and attempt to test them in separate environments. Because external consultants do not live with the consequences of breaking the system on a Monday morning, testing is slow and disruptive. Crucially, six months after the consultants leave, staff promotions and quick fixes begin again, and role creep quietly returns.
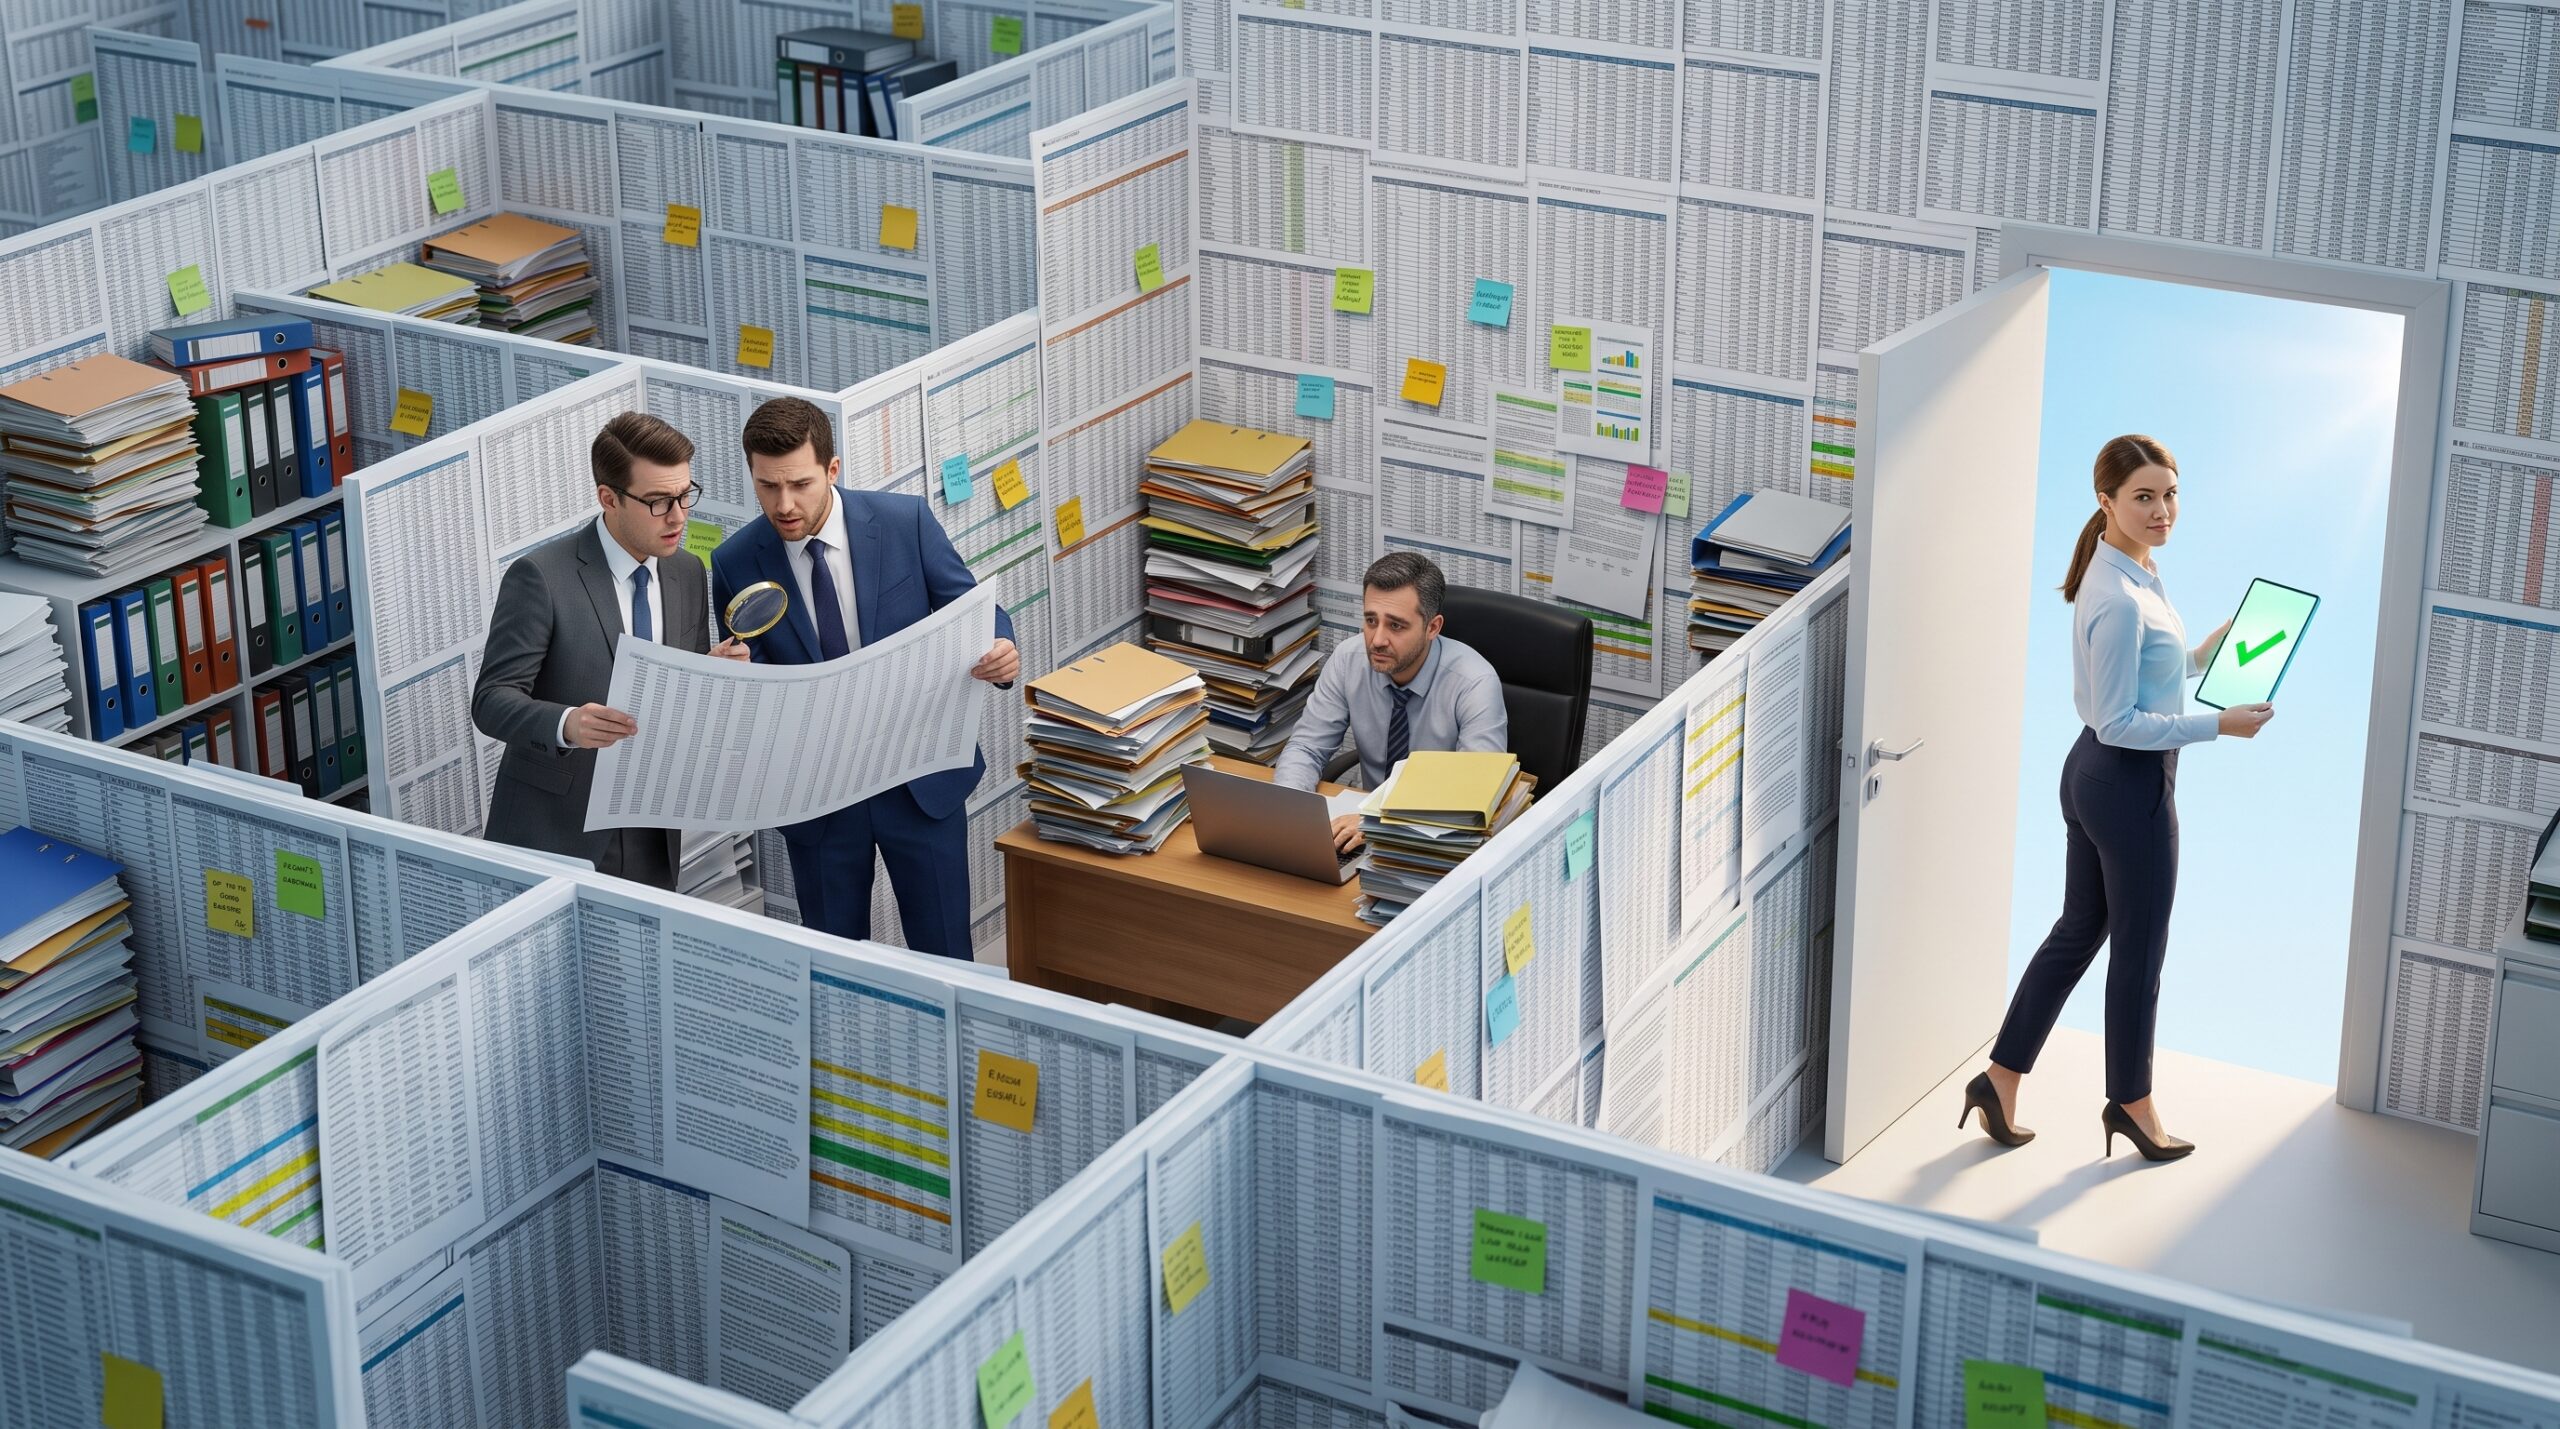
Lost in the spreadsheet labyrinth: manual workshops and contractor day rates drag on for months, while automated software gets your roles clean and audit-ready with minimal disruption.
| Approach | 1,000 Users Timeline | 10,000 Users Timeline | Estimated Project Cost | Business Disruption | Long-Term Result |
|---|---|---|---|---|---|
| Internal IT Team | 6 to 9 months | 18 to 24 months | £60,000 to £180,000 in diverted staff time | Moderate (workshops and testing meetings) | Role creep returns within 6 months |
| External Consultants | 3 to 5 months | 9 to 14 months | £150,000 to £1,200,000+ in day rates | High (heavy user testing cycles) | Static snapshot that quickly goes out of date |
| TangoTec Cortex Suite | 2 to 4 weeks | 6 to 8 weeks | Predictable software investment | Minimal disruption and minimal downtime | Permanent continuous governance via audit ledger |
The Solar Orbit: Shining a Light on the SAP Blind Spot
Instead of running manual workshops or guessing what people need in spreadsheets, we surround the dark SAP problem with five shining suns. Each module acts like a beam of sunlight burning away the fog, cutting through the confusion with real-world facts:
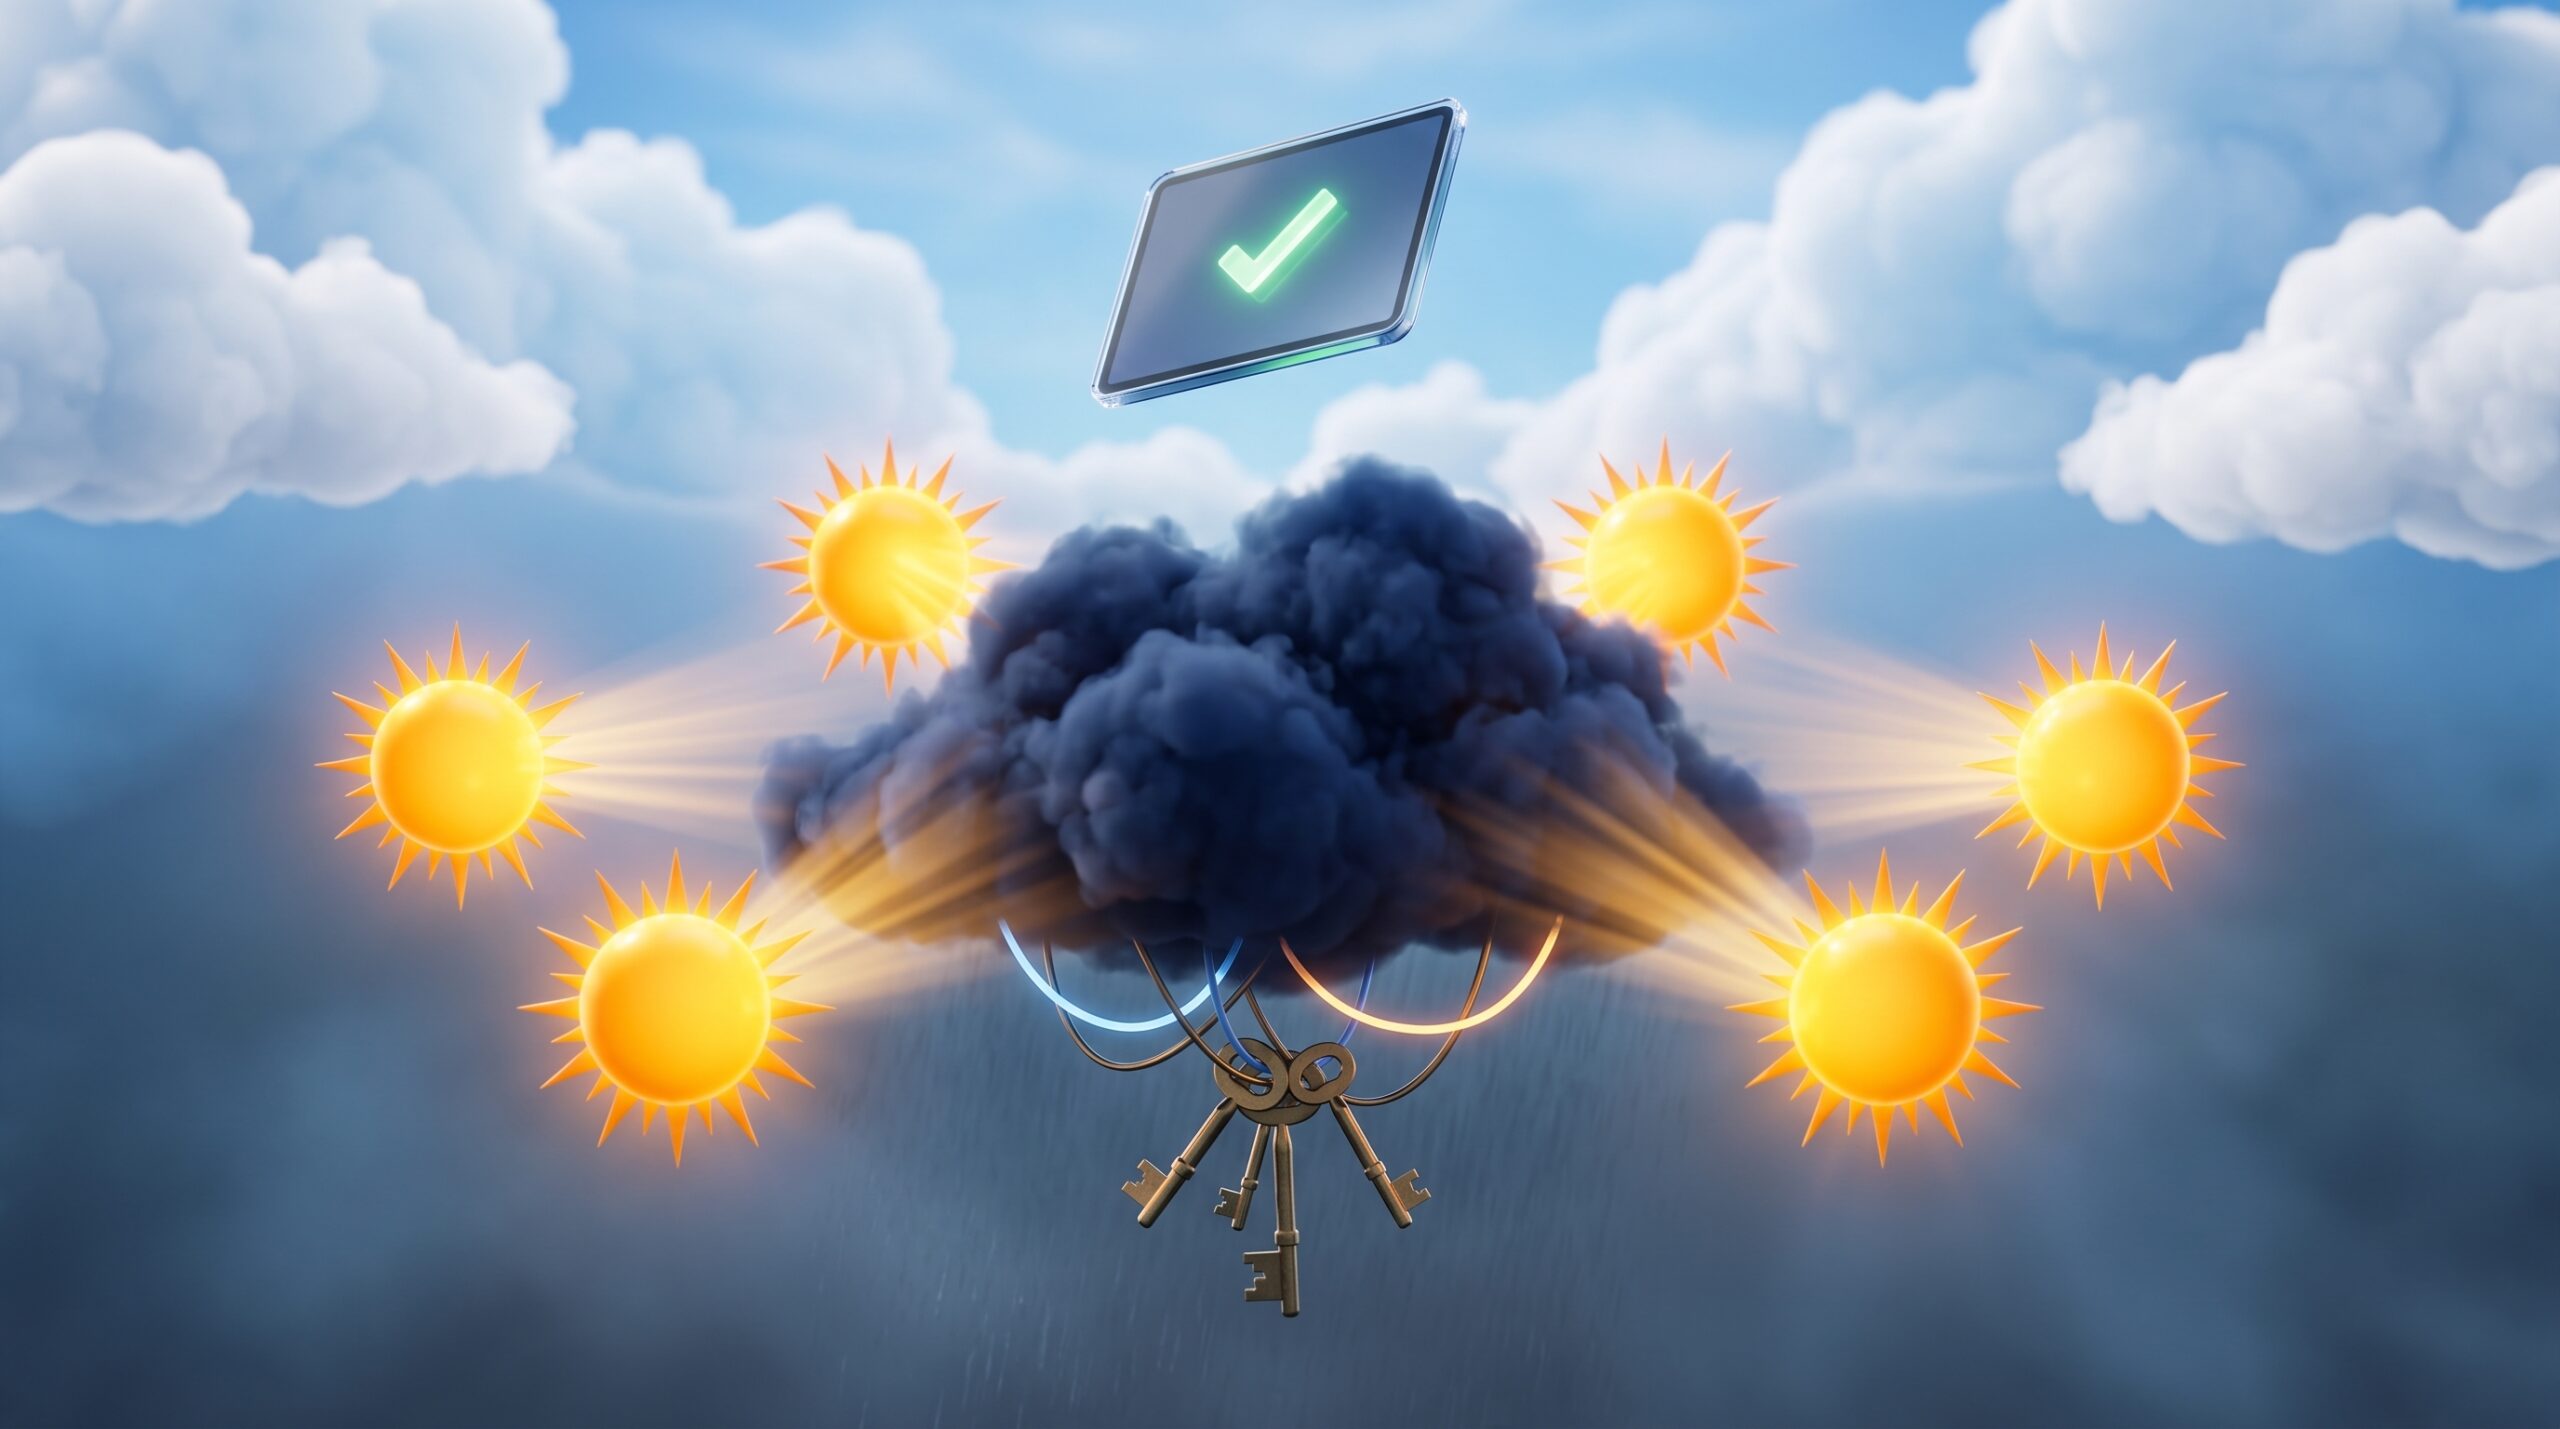
The weather clearing over your SAP landscape: five radiant Cortex modules shining their light onto the central blind spot, burning away licensing fog and audit panics.
The SAP Blind Spot
Paying for what users could do on paper, rather than what they actually do on screen, causing massive licence waste and audit panics during an S/4 HANA migration.
Measure Actual Usage
We run actual user activity through empirical behavioural gates, mathematically proving the lowest tier each person genuinely needs for an optimised S/4 HANA migration.
Build Clean Roles
We translate real task history into lean S/4HANA and Fiori roles, testing them quietly in the background with minimal downtime to accelerate your S/4 HANA migration.
Retain System Memory
We store years of compressed execution logs, giving you an unalterable memory bank of who did what, when, and how often.
Harvest Dormant Waste
The system systematically sweeps for inactive users and unexecuted permissions, safely pruning them to recover wasted cash before S/4 HANA migration cutover.
Visualise Real Risk
We replace dense spreadsheet matrices with a clear visual command centre, separating theoretical paper conflicts from real-world threats.
Separating Paper Panic from Real-World Risk in an S/4 HANA Migration
One of the biggest breakthroughs our clients experience is moving away from theoretical risk. Standard SAP governance tools tend to generate terrifying, thousand-row audit spreadsheets showing conflicts that someone could technically trigger if they decided to run every transaction in their job profile on the same afternoon.
In the real world, someone in billing might have held access to create vendors five years ago during an office move, but they have never once touched that screen since. Standard tools still flag that as an active corporate fraud risk. That leads to months of meetings, stress, and wasted engineering hours chasing paper ghosts during an S/4 HANA migration.
When we link Cortex VAULT with Cortex INSIGHT, we look at actual historical logs. We can show auditors that while the user had the theoretical capability, the conflicting transactions were never executed together. That lets your team focus their energy entirely on genuine, active risks, cutting audit noise by more than 80% and giving the board complete peace of mind throughout your S/4 HANA migration.
The Modular Cortex Toolkit for S/4 HANA Migration
Because every SAP estate is at a different stage of maturity, we built the TangoTec Cortex Suite natively inside SAP ABAP. That means there are no external servers to build, no separate databases to licence, and no complex integration projects. Enterprises can deploy the individual modules they need today, and expand them as their S/4 HANA migration journey evolves:
Analyses user activity against SAP’s FUE model, preventing overspending and eliminating Digital Access liabilities.
- FUE classification reduction
- Indirect usage audit protection
Provides clear visual risk analytics for Segregation of Duties (SoD), enabling compliance officers to pinpoint and remediate access conflicts.
- Visual SoD conflict mapping
- Automated access certifications
Automates migration from legacy ECC transaction codes to S/4HANA Fiori catalogues, architecting clean, least-privilege roles.
- Automated Fiori mapping
- Least privilege role builds
Captures deep execution intelligence to predict security bottlenecks, uncover dormant permissions, and keep projects on schedule.
- Predictive migration analytics
- AI-driven role remediations
Monitors SAP landscapes continuously to detect active cyber threats, unauthorized system changes, and suspicious user behaviour.
- Real-time threat detection
- Behavioural anomaly alerts
Powers emergency privileged access (Firefighter), automated identity lifecycle requests, and rigorous audit trails during cutover.
- Integrated Firefighter access
- Time-bound emergency audit logs
Unifies security, licensing, and risk data across all Cortex modules into a single-pane executive dashboard for complete visibility.
- Unified executive dashboards
- Cross-module audit reporting
Combines operational precision, commercial licence protection, and continuous GRC compliance into one cohesive ecosystem for S/4HANA.
Enterprise Reality: What Happens When You Use Hard Data in an S/4 HANA Migration
After a decade or more of business changes, almost every enterprise SAP system suffers from significant authorisation bloat. Unused transaction codes, dormant user accounts, and over-privileged roles quietly accumulate in the background. When organisations evaluate real historical usage instead of assumptions, they consistently achieve these verified outcomes:
Leave a Reply