Do We Really Need One?
A moment at your desk
You’re staring at a blank naming field in SAP, wondering whether an SAP role naming convention actually impacts your security posture. Having spent over 30 years reviewing SAP landscapes, I hear the same question constantly: If every role name must be unique anyway, why fuss over the naming structure?
A well-architected naming convention saves hundreds of administrative hours, prevents critical security breaches, and provides instant proof of compliance during an external SAP audit. In modern S/4HANA and RISE environments, role names are a foundational layer of governance that defends against risk and stops accidental licence cost inflation.
Common SAP role naming mistakes
Over three decades of security reviews, I’ve seen every flavour of naming mistake. Here are three common culprits that make security architects and auditors wince:
- Numeric-Only Names (e.g., Z0000001, Z0000002): Designed to force administrators to inspect role contents rather than rely on labels. Clever in theory; disastrous in practice. It solves a non-problem and slows down daily security operations
- Hardcoding Organisational Levels (e.g., Plant 1000 in the Name): Extremely brittle and ambiguous. When an employee spans multiple plants or company codes, these names create massive role proliferation and administrative confusion
- No Standard at All (“Making names up as we go”): Guarantees failed audits, uncontrolled role creep, and elevated Segregation of Duties (SoD) risks
Core requirements of a practical SAP security naming policy
A usable, audit-ready naming policy must accomplish five key technical goals:
- Facilitate Segregation of Duties (SoD) analysis and risk management
- Prevent accidental assignment of sensitive or emergency privileges in production
- Support strict transport paths across Development (DEV), Quality (QAS), and Production (PRD)
- Integrate natively with SAP authorisation objects like S_USER_SAS and S_USER_GRP
- Be policy-driven and digitally enforced across all PFCG builds
The Tango Standard: A 5-Part SAP Role Naming Framework
To balance readability, enforceability, and deep integration with native SAP authorisation checks, adopt this compact, policy-driven naming structure:
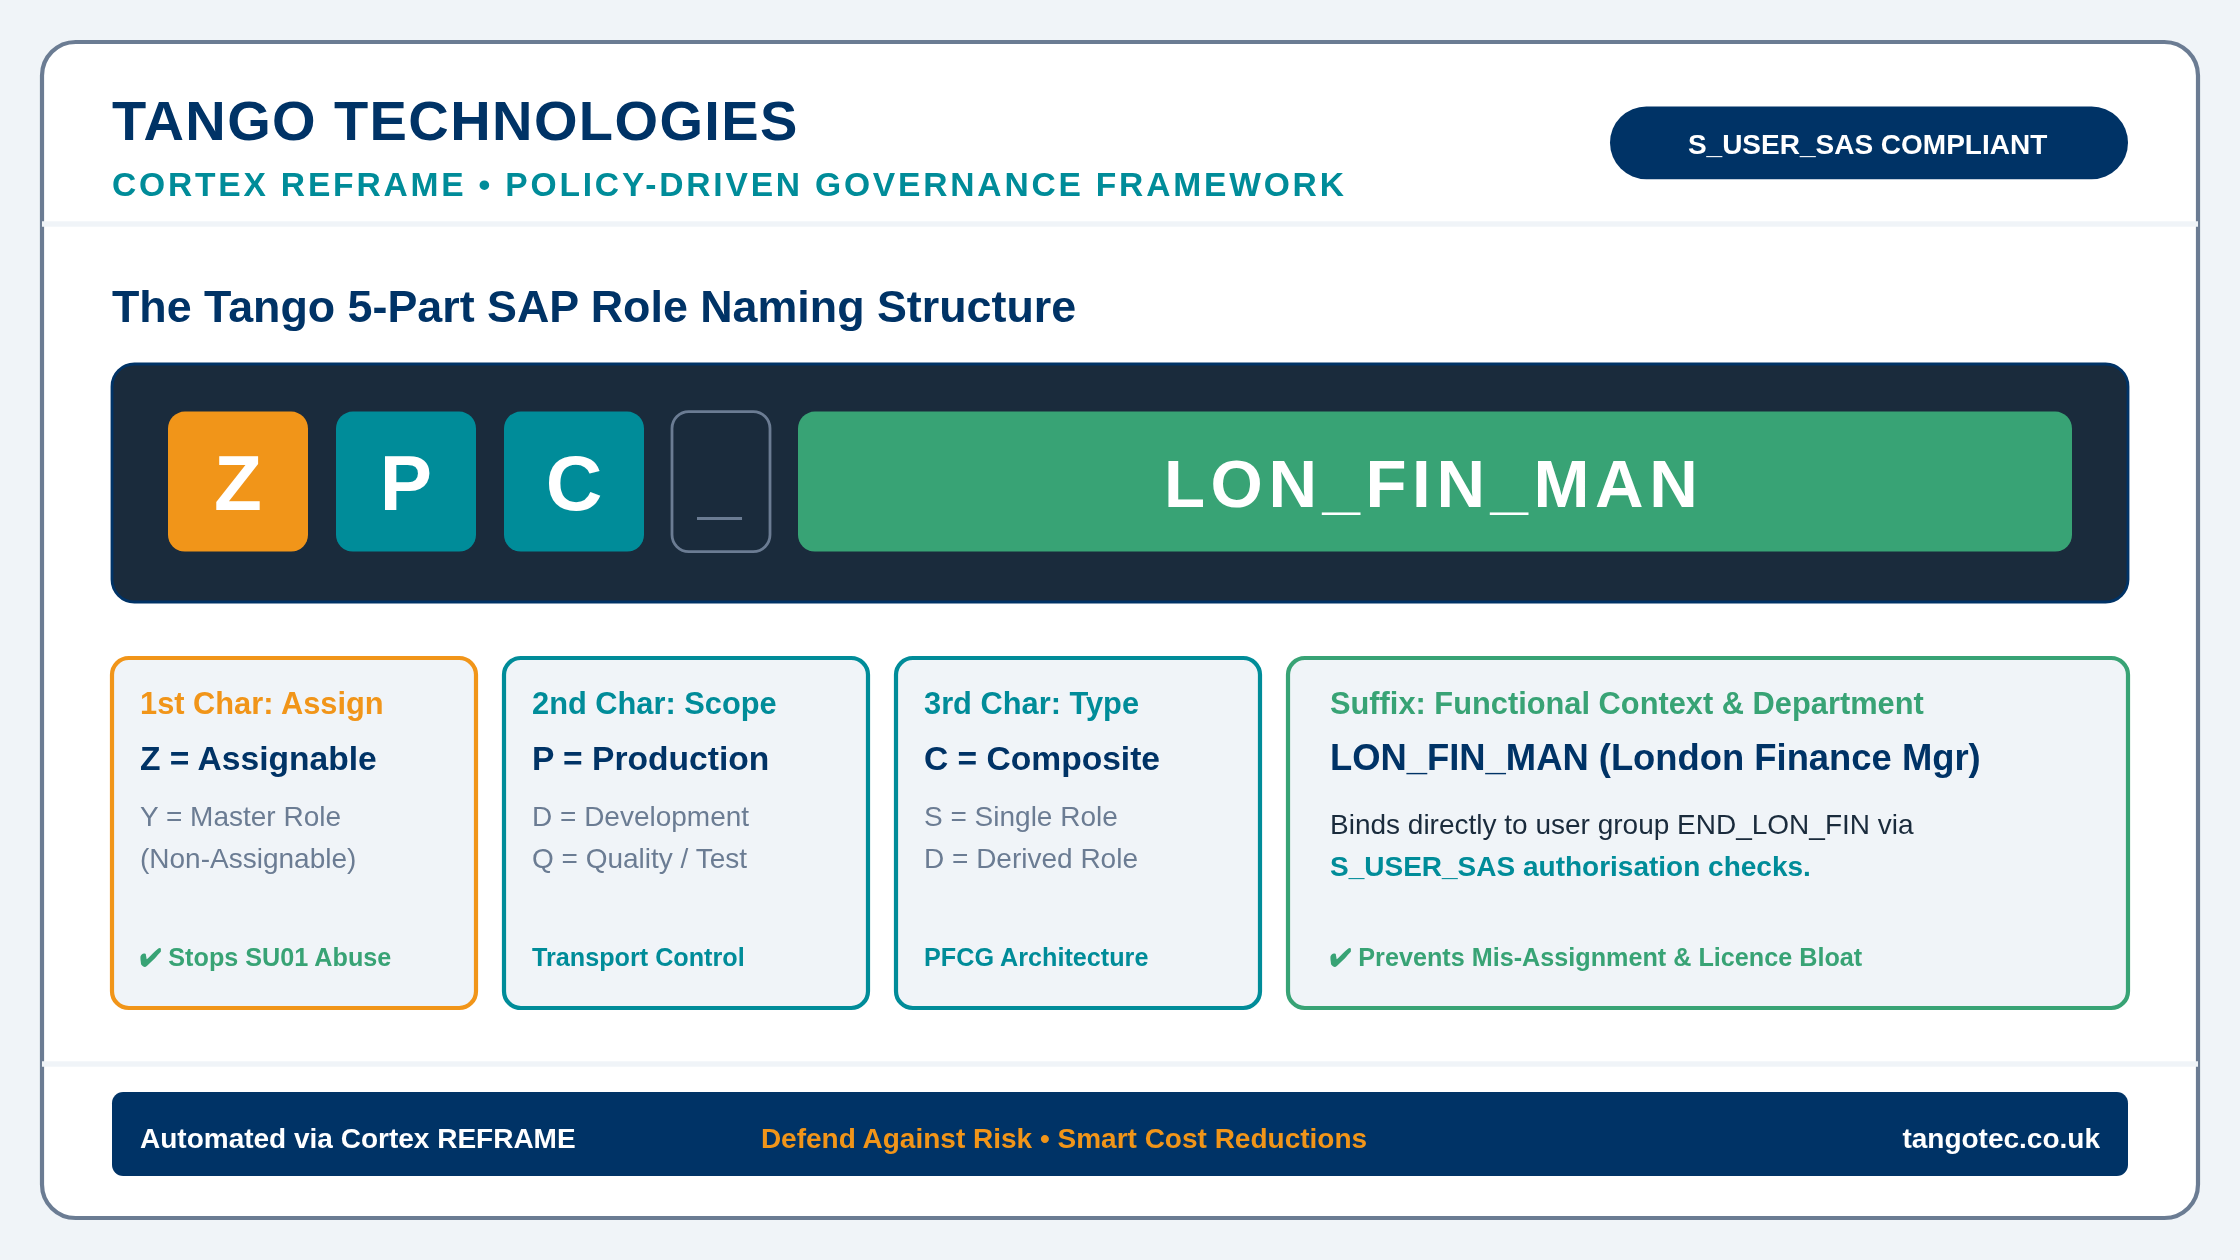
[Assignability][Transport Scope][Role Type]_[Business Area]_[Department]
- 1st Character (Assignability): Y = Master Role (non-assignable shell), Z = Assignable Role
- 2nd Character (Transport Scope): D = Development only, Q = Quality/Testing, P = Production assignable. This strictly governs transport path boundaries
- 3rd Character (Role Type): S = Single Role, D = Derived Role, C = Composite Role
- 4th Character (Separator): Underscore (_) for clear system readability
- 5th+ Characters (Business Area & Department): Agreed functional suffix (e.g., LON_FIN for London Finance)
Examples in Action:
- ZPC_LON_FIN… — Composite role, assignable in Production, for London Finance
- ZQD_WOR_HCM… — Derived role, assignable in Quality, for Worcester HR testing
- YDM_XXX_SAL… — Non-assignable Master role residing only in Development, used to derive regional sales access
Tying role names to automated SAP authorisation controls
By aligning role names directly to business policy, you can enforce security controls using native SAP authorisation objects. When end-user groups are named systematically (e.g., END_LON_FIN), the S_USER_SAS authorisation object restricts administrators so they can only assign roles matching that specific user group prefix.
This programmatic control prevents administrators from accidentally assigning global finance access to a local warehouse user, even if the request was approved in error. The naming convention becomes an active security control rather than a cosmetic tag.
Automating governance with the Tango Cortex Suite
While defining a policy is essential, manually enforcing standard names across thousands of PFCG roles is slow and prone to human error. Tango Technologies eliminates this burden by embedding best practices into our automated Cortex Suite:
- Cortex REFRAME (Role Design & Maintenance): Automatically enforces this 5-part naming convention during position-based role generation, eliminating naming deviations at source while converting legacy ECC transactions into modern S/4HANA Fiori equivalents.
- Cortex ECHO (SAP Licence Optimisation): Clear naming helps administrators verify access intent before provisioning. Paired with ECHO’s High-Watermark engine, it prevents users from accidentally receiving roles that trigger expensive S/4HANA FUE “Advanced” licence tiers.
- Cortex INSIGHT (Visual GRC): Replaces opaque database logs with a visual Risk Command Centre, cross-referencing cleanly named roles to catch Segregation of Duties (SoD) conflicts before live deployment.
- Cortex VAULT (Execution Analytics): Captures multi-year system activity and background trace data, cross-referencing real transaction execution against role names to provide external auditors with bulletproof proof of compliance.
Setting a structured naming policy reduces mis-assignments, speeds up audit clearance, and ensures your SAP security landscape is built for long-term stability.
Frequently Asked Questions (FAQ)
Why should Master Roles start with ‘Y’ and Assignable Roles with ‘Z’?
Distinguishing master roles (Y*) from assignable roles (Z*) at the first character level prevents administrators from accidentally provisioning unpopulated master shells directly to end users in SU01, keeping master templates clean and auditable.
How does an SAP role naming convention prevent licence cost inflation?
Structured naming makes transaction scope clear. Under SAP RISE and S/4HANA FUE models, assigning a role with a single unmonitored “Advanced” transaction code (like ME21N or FB60) can instantly escalate a user’s licence tier from 0.2 FUE (Core) to 1.0 FUE (Advanced). Structured names help administrators spot over-privileged roles before assignment.
Can Cortex REFRAME rename existing legacy SAP roles automatically?
Yes. Cortex REFRAME includes automated role lifecycle utilities (Copy, Merge, Rename, and Transport) that allow security teams to mass-rename legacy PFCG roles to align with compliant naming standards while preserving underlying authorisation data.
Yes. Cortex REFRAME includes automated role lifecycle utilities (Copy, Merge, Rename, and Transport) that allow security teams to mass-rename legacy PFCG roles to align with compliant naming standards while preserving underlying authorisation data.