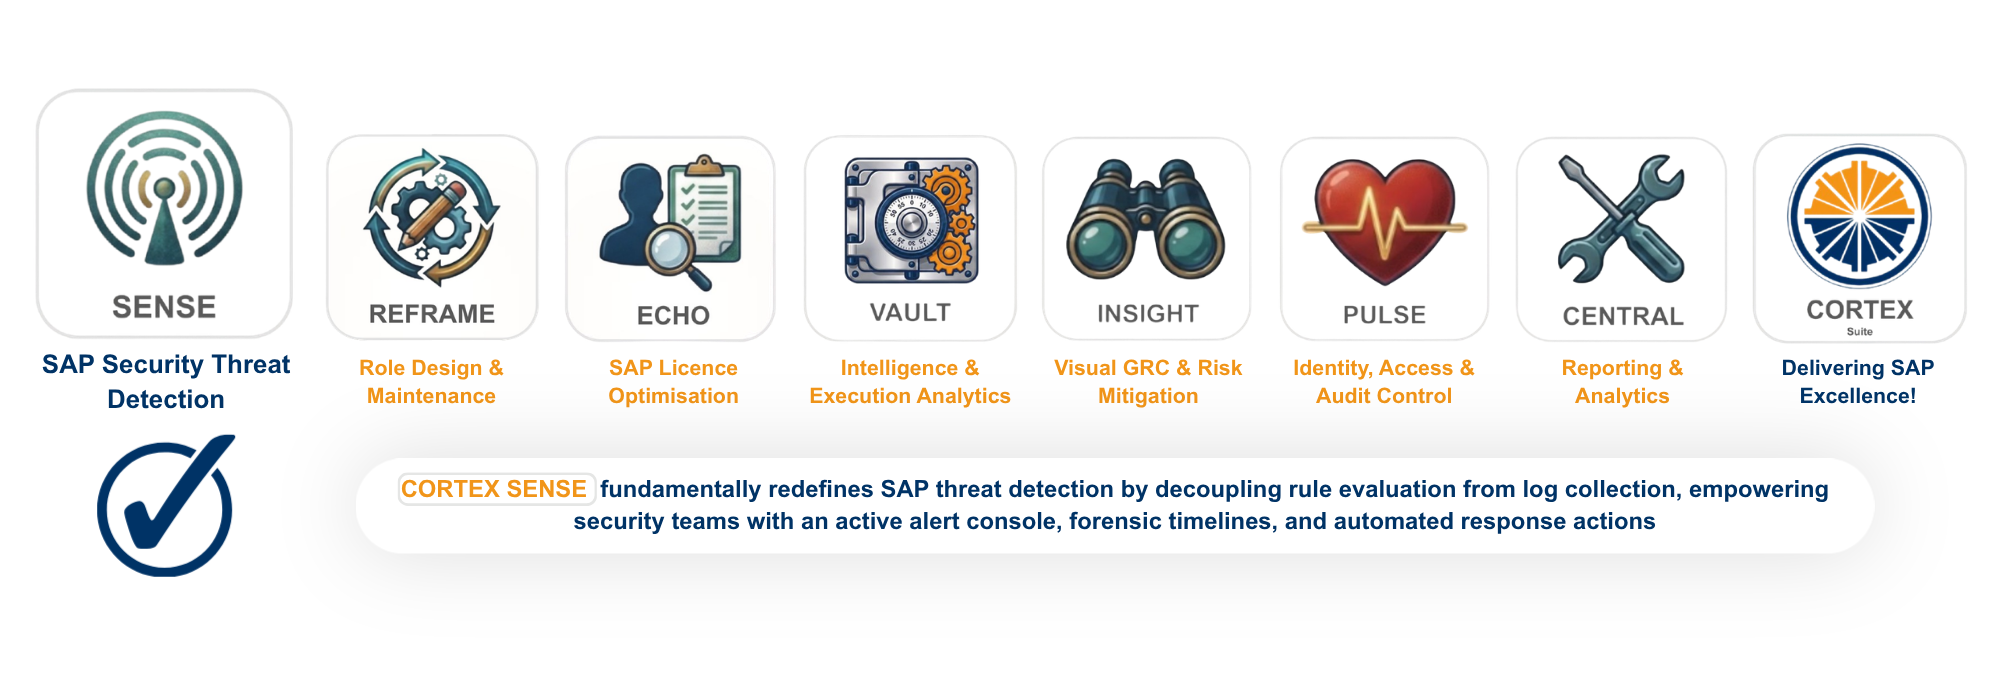
CORTEX SENSE Fundamentally Redefining SAP Threat Detection & Audit Log Analysis
Cortex SENSE delivering real-time operational clarity across all managed systems!
Redefining SAP Threat Detection
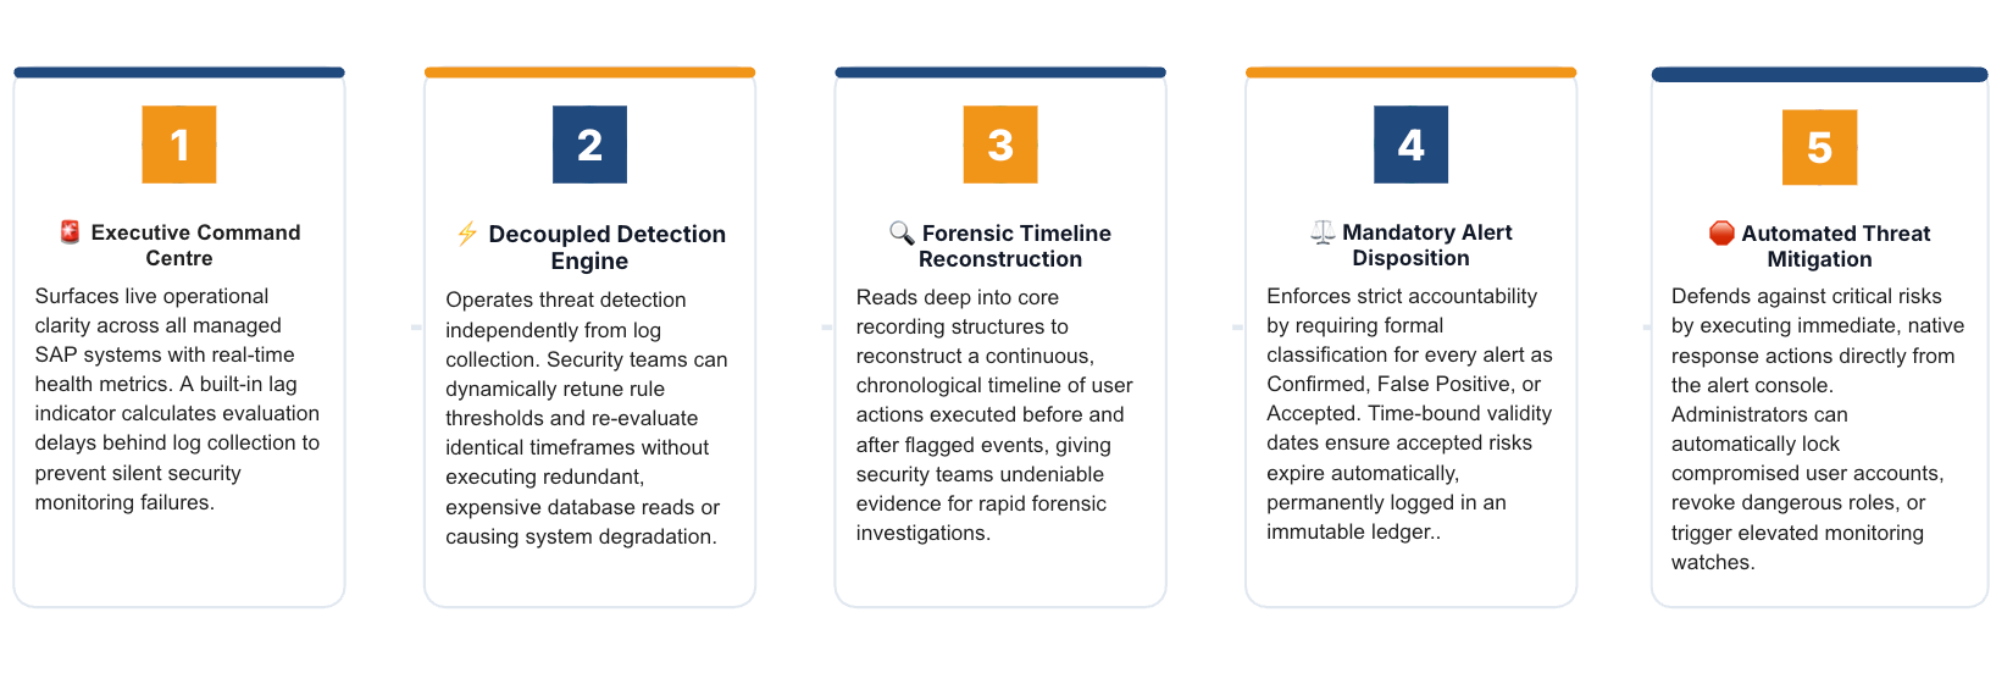
Operating through an executive command centre, SENSE delivers immediate visibility across your entire landscape. It surfaces live health metrics, open alerts, enabled rules, and total detection items directly within a unified launchpad. By moving away from complex menu trees, your security teams gain an intuitive, focused workspace that highlights critical threats the moment they occur, perfectly supporting our core mission to expertly customise secure solutions that defend against risk.
At the heart of SENSE is a revolutionary decoupled architecture. By completely separating the threat detection engine from log collection, your security teams gain maximum tuning flexibility. Analysts can actively retune rule thresholds and re-evaluate historical periods without ever needing to execute redundant, expensive database reads, dramatically reducing system overhead.
Our high-performance collection engine streamlines this process further by capturing only what is strictly necessary. Utilising targeted log sweeping, SENSE rapidly interrogates managed SAP systems by dynamically reading active rule matrices. This ensures it exclusively extracts logs required by your active rules, while an integrated automated housekeeping mechanism ages out and securely deletes historical data based on your specific retention windows.
To ensure your monitoring never silently fails, a built-in system lag early-warning indicator calculates the exact duration your evaluation lags behind log collection. Combined with in-app settings governance that utilises strict delete-and-insert mechanisms to eliminate duplicate entries, SENSE provides total control over detection sensitivity, system scope, and operational health.
Actionable, Evidence-Backed Security Interventions
SENSE, built to deliver immutable decision tracking!
Securing Your Audit & Incident Response
The Active Alert Console within SENSE forces strict accountability by ensuring every security decision is backed by concrete proof. A unified evidence and decision view displays raw audit rows and historical logs directly alongside your response actions. This allows analysts to make critical security decisions based on highly visible, undeniable proof rather than assumption.
To eliminate silent closures, the system utilises mandatory disposition enforcement. Operators are required to assign a formal classification; Confirmed, False Positive, or Accepted Risk, to every single alert. This ensures that no potential threat is swept under the rug and that your security operations remain completely transparent and audit-ready.
When exceptions are necessary, SENSE governs them through strict time-bound risk acceptance. Administrators must assign explicit validity end-dates to accepted risks, ensuring that these exceptions automatically expire rather than hiding indefinitely within the system. Every single event, status change, and piece of evidence is permanently recorded in an append-only, immutable alert ledger, guaranteeing a rapid, fully compliant audit result.
For deeper investigations, the forensic timeline reconstruction feature reads deep into core recording structures. It displays a continuous, chronological sequence of user actions executed both before and after any flagged incident occurs. This allows your security teams to reverse-engineer events, understand the full scope of a vulnerability, and provide auditors with unquestionable, step-by-step evidence.
To defend against risk and mitigate threats immediately, SENSE integrates directly with Access Hubs to execute automated response actions directly from the alert console. Security teams can dispatch native requests to lock compromised user accounts, instantly revoke specific dangerous roles, or flag suspicious profiles for proactive watch and elevated tracking over defined timeframes.